

August 2026: One Device, All the Damage
3 views
Blog august2026 · TXT
AUGUST 2026 — BLOCKCHAIN THREAT INTELLIGENCE REPORT
$204,026,958 lost across 55 incidents. One hardware outlier. Three zero-day clusters. The supply chain is broken.
September 4, 2026 Monthly Report Threat Intelligence
TL;DR
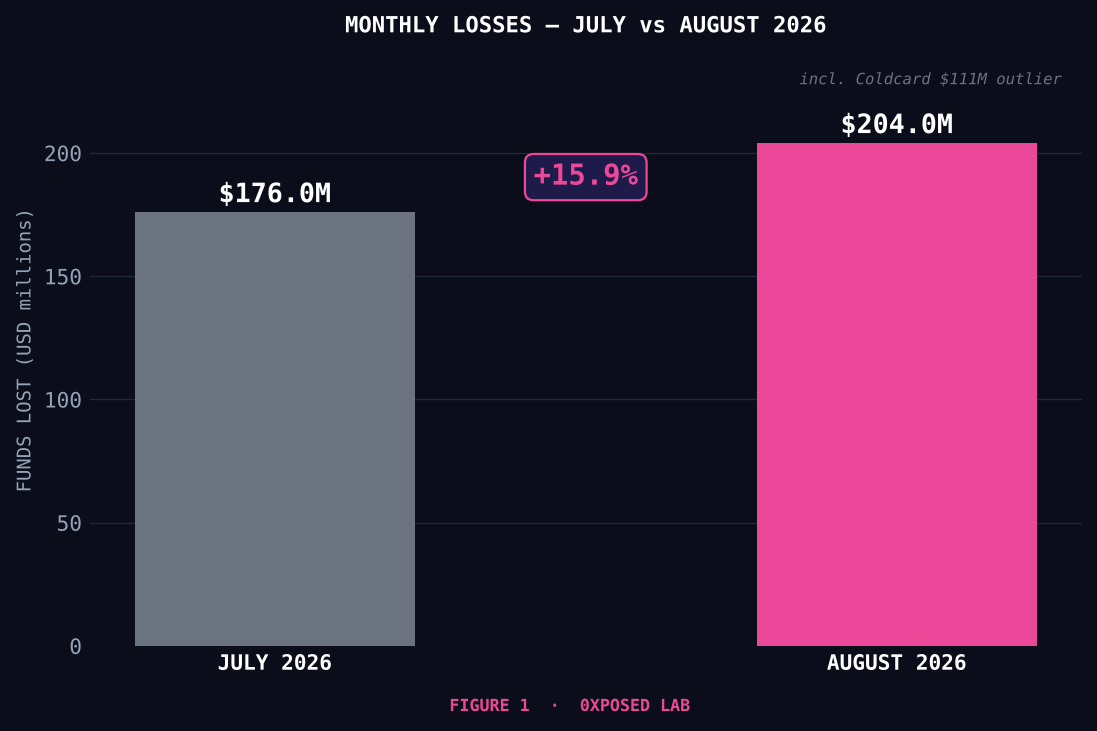
August 2026 recorded $204,026,958 in confirmed losses across 55 incidents — a +15.9% increase over July 2026 ($176.1M). Strip the Coldcard hardware outlier ($111M), and the residual ecosystem loss stands at $93M across 54 incidents: a figure that is itself alarming. Three distinct zero-day clusters — Cosmos EVM shared module (GHSA-7g4w-cg88-2cq2), Switchboard oracle signing key compromise, and a simultaneous wave of developer-tooling supply chain attacks spanning npm, Rust crates.io, VS Code extensions, and hardware wallet firmware — make this the most structurally concerning month of 2026. Recovery stands at $0 formally recovered from confirmed financial losses. Funds are not coming back.
SECTION 1 — AGGREGATE OVERVIEW
55 incidents. $204,026,958 total. $93,026,958 ex-Coldcard. The headline figure for August is dominated by a single event unprecedented in hardware wallet history: a confirmed RNG firmware vulnerability in Coldcard hardware wallets, resulting in $111,000,000 in confirmed on-chain drains. That figure alone accounts for 54.4% of all August losses. Removing Coldcard, the August 2026 ecosystem still generated $93M in losses. 39 of 55 incidents carried confirmed financial impact; 16 incidents recorded zero direct financial loss but qualify as significant security events: data breaches exposing ~253,487 user records across three custodians, infrastructure compromises of critical developer tooling, and supply-chain attacks targeting Web3 developers. Weekly distribution:
Week 1 (Aug 1–7): $115,458,172 — 56.6% of monthly total (Coldcard disclosure)
Week 2 (Aug 8–14): $42,165,996 — 20.7% (TLBL whale, Coinsbuy, Harmony)
Week 3 (Aug 15–21): $6,634,918 — 3.3% (FoxMarket, BounceBit, Maya, Tornado Cash phish)
Week 4 (Aug 22–31): $39,767,872 — 19.5% (Moonwell, Term Finance, Tectonic,
SECTION 2 — INCIDENT CATALOG BY TIER
── TIER 1 · CATASTROPHIC (> $25M) ──
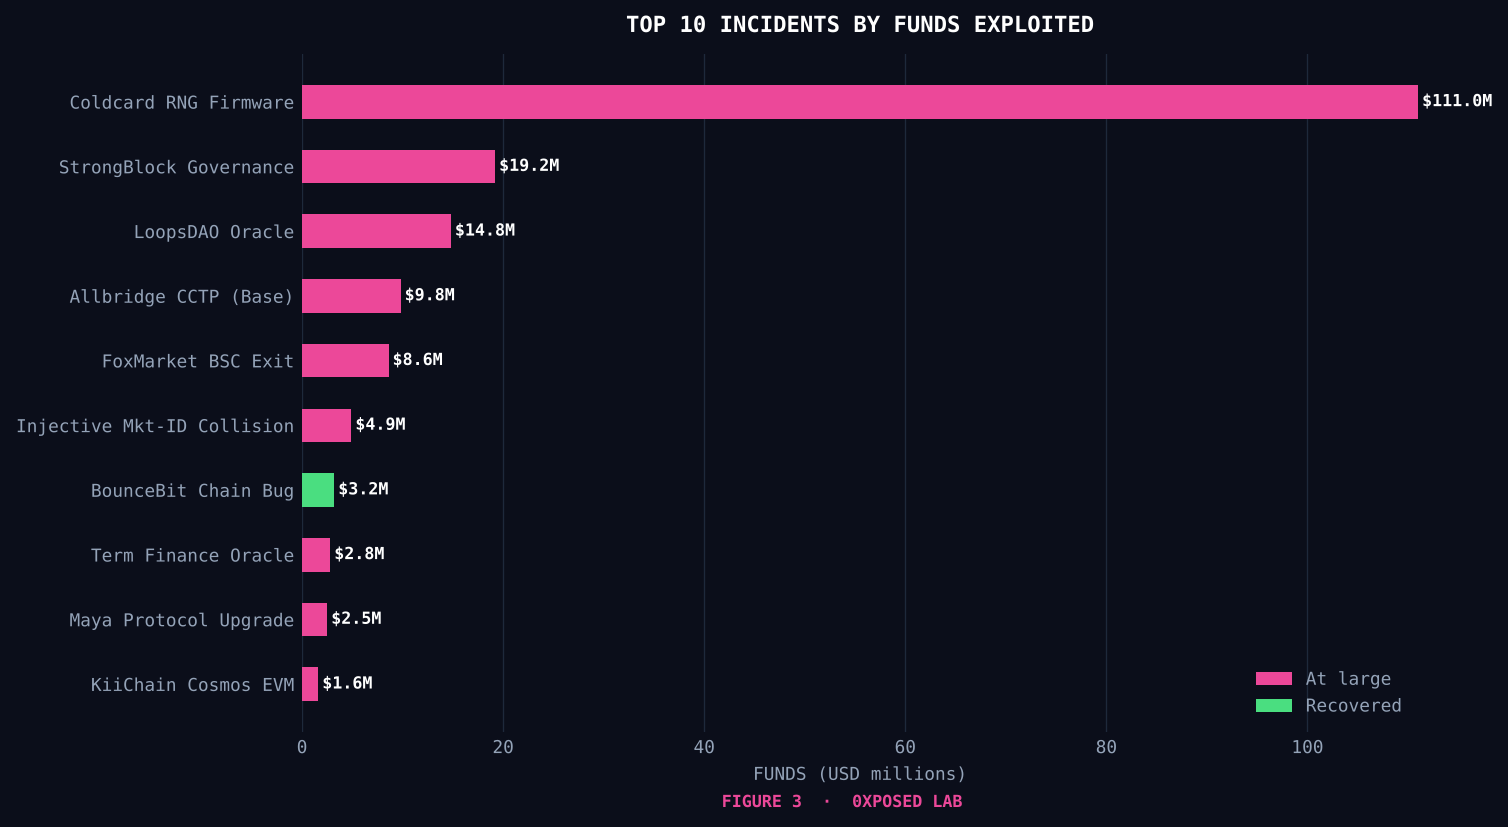
#01 · Coldcard Firmware RNG
Vulnerability — $111,000,000August 7, 2026 · Bitcoin · Private Key Compromise · Status: Active The defining incident of August 2026. Coinkite's Coldcard hardware wallet — one of the most trusted Bitcoin signing devices in the industry — was found to have shipped a critically weakened random-number generator since firmware version 4.0.1 (March 17, 2021, block ~674,951). A commit dated March 1, 2021 silently replaced the hardware TRNG call ckcc.rng_bytes() with a software PRNG seeded from a 32-byte XOR of seven entropy sources — a flawed combination that reduced effective entropy to approximately 48 bits in the worst case. Wallets generated on affected firmware could have their private keys reconstructed by an attacker with moderate compute resources. Disclosure came on August 7, 2026, coordinated with a Coinkite security bulletin and coverage from Galaxy Research (Alex Thorn). At least fifteen distinct attackers were identified by Galaxy, draining across two waves. Known consolidation addresses hold approximately 1,158.66 BTC as of the disclosure date, with roughly 90% unmoved — consistent with patient, structured extraction. Confirmed loss: $111,000,000.
#02 · TLBL Whale — Private Key Compromise & DeFi Position Drain — $25,600,000August 12–16, 2026 · Ethereum L1 · Status: Active The on-chain entity labeled "TLBL" by Lookonchain — a veteran Ethereum whale with a 5+ year wallet history — suffered a private key compromise beginning August 12. At least three wallets were systematically drained in a structured unwinding of DeFi positions: approximately $20M in DAI and ~3,000 ETH (~$5.64M) consolidated across four or more attacker-controlled addresses. The compromise method was consistent with native private key extraction (exfiltration of key material, hardware attack, or operational security failure) — phishing was ruled out. Total confirmed loss: $25,600,000.
── TIER 2 · MAJOR ($5M–$25M) ──
#03 · Tectonic Finance — Donation-Attack Price Manipulation (Cronos) — $9,190,000August 30, 2026 · Cronos · Status: Contained On August 30 at 12:38:56 UTC, an attacker executed a donation-attack style price manipulation against Tectonic Finance's money-market protocol on Cronos. Gross amount manipulated: ~$120M in inflated collateral; net protocol loss: $9,190,000. Attack duration: approximately 114 minutes. Funds consolidated to Ethereum address 0xc404160b79bd8905061a1... Attacker operator: 0x4266a0e6a0f0ef90abcff3bb089932ca0cce3652 (on-chain confirmed).
#04 · Moonwell MAMO Market — Oracle Manipulation & Bad Debt (Base) — $9,131,342August 27, 2026 · Base (Ethereum L2) · Status: Contained Between 06:09:45 and 09:30:13 UTC on August 27, an attacker manipulated Moonwell's MAMO lending market on Base via a donation-style oracle manipulation that bypassed the protocol's supply cap. Exploiter 1 (0x719eae70d4A83f35bF82A2740699F5db84BE919D) and a funding wallet executed the attack. Funds converted through Maker PSM and Velora/AVNU aggregator swaps into DAI/USDC. Confirmed bad debt: $9,131,342 — absorbed by protocol reserves.
#05 · Term Finance — Governance Takeover via Malicious Proposal — $8,500,000August 23, 2026 · Ethereum · Status: Contained Two coordinated attacker wallets (Exploiter 1: 0xa908b3472d76e7744baB0A5911768a4a6300612B; Exploiter 2: 0x686457a7468B9B31c5dbA43b1b16..., both pre-funded via Tornado Cash) executed a governance takeover of Term Finance's ETH Meta Vault. Eight malicious governance proposals passed via threshold exploitation, draining $8,500,000. Funds consolidated at 0xD5183d8BfC65a50863C62aF2538198A8288FFc13 and subsequently laundered via a dedicated hub wallet.
#06 · Coinsbuy — Coordinated Multi-Chain Hot Wallet Drain — $7,900,000August 9, 2026 · Ethereum + TRON · Status: Resolved On August 9 at 12:43:09 UTC, Coinsbuy — a B2B crypto payment processor — was drained of $7,900,000 across Ethereum and TRON in a coordinated multi-chain attack that began with a 5 USDT test transaction on TRON. Attacker ETH hub: 0x4d1bEF2Fe998B3E3C4029EF9EA6A0534d95661d3. Approximately 79% of funds ($6.34M) routed via FixedFloat using ~50 single-use addresses. Coinsbuy continued operations through cold wallet reserves.
#07 · Tiffany Milanovich — Crypto Support Impersonation Fraud Network — $5,000,000August 10, 2026 · Bitcoin + Ethereum + Coinbase · Status: Active On August 10, ZachXBT published a detailed investigative thread naming Tiffany Milanovich (US-based) as the operator of a multi-victim crypto support impersonation fraud network responsible for more than $5,000,000 in cumulative thefts. Operating through the Telegram fraud marketplace t.me/edge (10% proxy fee), the network posed as exchange and wallet support agents to harvest seed phrases and remote access. Known stolen Bitcoin held at bc1qw3mej... and bc1q2r2t...
── TIER 3 · SIGNIFICANT ($1M–$5M) ──
#08 · Injective — Binary Options Market-ID Hash Collision — $4,900,000August 31, 2026 · Injective / Ethereum · Status: Active An attacker exploited a market_id hash collision in Injective's permissionless binary options market creation system — Injective generates market_id by concatenating oracle fields without separators, enabling collision. $4,900,000 converted to ETH and bridged via CCTP to Ethereum, consolidated at ~1,980 ETH. Injective halted for 3h42m (16:10–19:52 UTC). No official post-mortem published.
#09 · BounceBit Chain — Evmos Authorization Flaw — $3,300,000August 19–21, 2026 · BounceBit Chain (standalone Evmos-based L1) · Status: Closed Beginning at block 20,697,260 (Aug 19, 21:02 UTC), an attacker exploited a protocol-level authorization flaw in BounceBit's Evmos-based L1, debiting nine ordinary accounts without holding their keys. Attack duration: approximately 4 hours 52 minutes. Total loss: $3,300,000. BounceBit permanently sunset its standalone L1 and reissued BB tokens as BEP-20 on BNB Chain using a pre-attack snapshot.
#10 · Harmony Protocol — Unauthorized 4B ONE Mint via Cross-Shard Receipt Replay — $3,200,000August 11–14, 2026 · Harmony L1 · Status: Recovering Two combined consensus bugs enabled unauthorized minting of approximately 4 billion ONE tokens (~26% of circulating supply). Realized market value: $3,200,000. 2,800,000,000 ONE was sent to KuCoin deposit address one1xk9fwdqqmgcrxnl68xlguqsef0lxt84kmdyzyk. Harmony coordinated with KuCoin to freeze incoming deposits. Chain recovery was underway as of August 14.
#11 · Tornado Cash Fake Frontend Phishing — 810 ETH — $1,860,000August 18–21, 2026 · Ethereum · Status: Active Attacker wallet 0xd8B356356d7B143D7ece9F5876FE4b954E93b745 (gas-seeded August 12 via Tornado Cash relayer) collected nine deposits — eight of 100 ETH and one of 10 ETH — via a phishing campaign deploying a fake Tornado Cash frontend. All 810.097 ETH remains held at the attacker address with zero outgoing transactions — consistent with a patient hold pending chain analysis cool-off. Total loss: $1,860,000.
#12 · KiiChain — Cosmos EVM Balance Underflow (GHSA-7g4w-cg88-2cq2) — $1,610,000August 22, 2026 · KiiChain (Cosmos EVM) · Status: Contained On August 22 at approximately 20:32 UTC, an attacker launched 18 separate exploit attempts against KiiChain using the shared Cosmos EVM module vulnerability GHSA-7g4w-cg88-2cq2. KiiChain's post-mortem confirmed the extraction figure: 148,326,583.15 KII tokens — the only one of the three affected chains to publish exact volumes. Realized loss: $1,610,000. → See Cluster Analysis Section 3
#13 · Trezor Google Ads Phishing — Seed Phrase Harvesting — $1,600,000August 6–7, 2026 · Bitcoin · Status: Active An attacker purchased a Google Ads sponsored placement for "Trezor wallet," directing victims to a fraudulent Trezor Suite website on Google Sites. The site harvested seed phrases entered by victims who believed they were completing a software update. 24.04135820 BTC (~$1,600,000) collected at bc1qrz33mr7tx8wrpcs2pxrvv83hqwpm907s9shkz4. This campaign ran concurrently with the Coldcard firmware disclosure, exploiting hardware-wallet anxiety.
#14 · Maya Protocol — Six-Bug MAYAChain Exploit — $1,356,218August 18–19, 2026 · MAYAChain (Cosmos SDK) · Status: Paused At block 17,977,941 (Aug 18, ~17:30 UTC), an attacker submitted a single 23-message MsgDeposit triggering a chained six-bug exploit: an uncapped slash subsidy mechanism enabling repeated extraction of liquidity pool reserves. Net extraction: ~48.87M CACAO + 98.82 ARB.LINK; BTC consolidated to bc1q0hsgwunccczelq05ucpmfz268eyy5jr2y5l646. Total: $1,356,218. MAYAChain halted the chain and paused all swaps.
#15 · Radix Vault — Engine-Level Authorization Vulnerability — $1,300,000August 31, 2026 · Radix · Status: Contained Between 16:02 and 16:57 UTC on August 31, an attacker exploited a bug in the core Radix Engine — present since June 2023 and undetected through a Zellic audit in August 2024 — allowing unauthorized vault withdrawals by bypassing Radix's native authorization checks. Loss: $1,300,000. The Radix Foundation declined to publish attacker addresses, referring exclusively to law enforcement (Jersey, UK jurisdiction).
#16 · Fogo Foundation — Private Key Compromise — $1,200,000 Net ($3M Gross)August 28–29, 2026 · Fogo (SVM chain) · Status: Contained A Fogo Foundation private key controlling 400 million FOGO tokens (~4% of genesis supply, ~$3M gross) was compromised. Approximately 163M FOGO tokens confirmed missing. Net loss after slippage: $1,200,000. The Fogo mainnet was halted at 01:13 UTC on August 29 and resumed following a validator-consensus-coordinated restart.
#17 · TAC — Cosmos EVM Balance Underflow (GHSA-7g4w-cg88-2cq2) — $1,005,774August 22, 2026 · TAC (Cosmos EVM) · Status: Contained At approximately 19:46 UTC on August 22, the first of three Cosmos EVM cluster attacks. Nominal on-chain value displaced: $7.5M; realized profit after bridging to BNB Chain and TON: $1,005,774. TAC halted at block 24,671,475. → See Cluster Analysis Section 3
── TIER 4 · MODERATE ($500K–$1M) ──
#18 · MOKE Token — Unprotected claim() Function — $907,700August 2, 2026 · BNB Chain · Status: Active The MOKE token protocol on BNB Chain was exploited via an unprotected public claim() function in MokeToken.releaseContract() with no eligibility check. Per SlowMist Hacked's official incident record: approximately 166 million MOKE tokens drained and converted for ~$907,700. MOKE token contract: 0x273b54cBAE81fC75193C1352f0b3667960f1F1B8.
#19 · Ajna Protocol V2 — Liquidation Accounting Exploit — $775,400August 28–29, 2026 · Ethereum · Status: Active An attacker manipulated liquidation accounting logic across seven separate Ajna Protocol V2 pools on Ethereum, extracting $775,400 total. Notably, Defimon had flagged the vulnerability pre-attack — the alert went unactioned. Because Ajna's contracts are immutable, affected pools cannot be patched. Pools affected: syrupUSDC, wstETH, rETH, cbETH, WBTC, WETH-USDC, sDAI.
#20 · LoopsDAO — Flash Loan Price Manipulation — $689,496August 2, 2026 · BNB Chain · Status: Closed Attacker 0x5d289266d85EF671561bA3F253FB79327C193f33 executed a flash loan of 730,607.75 USDC from Uniswap V4 Pool Manager at block 113,613,924, manipulating LpdFi's spot price to mint underpriced tokens and redeeming at market value. Net extracted: 689,529.79 USDC ($689,496).
#21 · RISEx — XLP Vault RWA Strategy Misconfiguration — $673,012August 3, 2026 · RISE Chain (Ethereum L2) · Status: Resolved A Real World Asset (RWA) strategy linked to RISEx's XLP vault was deployed July 13 with an access control misconfiguration. On August 3 at block 18,135,959, attacker 0xAAb85f96FeB6DaAc1E171e7e4B0118B16f1BB66d withdrew 673,011.565895 USDC.e via exploited contract 0x04a7934245c9B804082e391Ee077c130d31B10a5. Extracted: $673,012. Protocol subsequently resolved and communicated with affected users.
#22 · Base Wallet Drain via Steakhouse Prime Vault — $501,651August 6, 2026 · Base (Ethereum L2) · Status: Closed At block 49,597,025, attacker 0x920d3b63541eAFe13E05dc4f3453904102c39708 drained a victim wallet holding Steakhouse Prime (steakUSDC) Morpho vault positions: 501,940.006236 USDC. Classified as phishing/wallet compromise. The drainer was "sandwiched" by an MEV bot that front-ran part of the transaction — characteristic of Base's competitive MEV environment. Extracted: $501,651.
── TIER 5 · MINOR ($100K–$500K) ──
#23 · Virtue IOTA — Switchboard Oracle Key Compromise — $455,000August 28, 2026 · IOTA · Status: Contained Signing keys of 14 Switchboard oracles on IOTA mainnet were compromised, allowing the attacker to push manipulated price feeds to Virtue's CDP stablecoin protocol. 45 users liquidated across 47 liquidation events; 4.94M VUSD positions liquidated at artificial prices. Total loss: $455,000. → See Cluster Analysis Section 3
#24 · Realio Network — Multi-Chain Signing Key Compromise — $338,700 Net ($6.2M Gross)August 25, 2026 · Ethereum / BNB Chain / Algorand / Stellar / Realio L1 · Status: Contained A signing key controlling Realio Network's treasury across five chains was compromised. Gross on-chain displacement: ~129M RIO tokens (~$6.2M). Net liquid loss after illiquidity constraints and rapid protocol freeze: $338,700. No attacker addresses published; forensic data provided privately to law enforcement.
#25 · GOLD Token — Rug Pull / X Account Compromise — $330,000August 29, 2026 · Solana · Status: Contained A token marketed as GOLD, presented as linked to Donald Trump's digital asset ecosystem, was used in a rug pull enabled by a compromised X account. A cluster of 15 coordinated wallets simultaneously sold GOLD tokens for a realized $330,000. Token mint: EMWtbpHaNqMbjUMZguuazhuZUVLWG3z4C5oZnGJPSqxS. Token subsequently abandoned.
#26 · Ankr / ankrFLOW — Unbacked LST Mint via More Markets — $246,000August 31, 2026 · Flow EVM · Status: Contained A flaw in Ankr's ankrFLOW liquid staking token contract allowed minting without corresponding backing collateral. The unbacked LST was used as inflated collateral on More Markets to borrow real assets. Facial value of unbacked position: ~$410K; realized liquid loss: $246,000. More Markets paused all ankrFLOW collateral pools within hours.
#27 · Balancer V1 Legacy BPool — Rounding Exploit — $234,000August 30–31, 2026 · Ethereum · Status: Contained Attacker 0x338c7ec9befbb451d66fd8a468c32184f5689a41 exploited a rounding flaw in the legacy Balancer V1 BPool's joinswapPoolAmountOut() function. By repeatedly compressing the pool's WBTC reserves via flash-loaned capital from Spark and Aave, the attacker extracted $234,000 via accumulated rounding losses. Balancer V1 is immutable; Balancer DAO issued a formal deprecation notice.
#28 · Coreum/tx XRPL Bridge — Fake Deposit Relayer Logic Exploit — $200,000August 9, 2026 · XRP Ledger + Coreum/tx (Cosmos) · Status: Paused The XRPL↔Coreum (tx) bridge was exploited via a deposit verification logic flaw, draining 199,916.3 XRP (~$200,000, ~99.7% of reserves) across 94 multisig transactions in 97 minutes. The exploit involved submitting fake deposit messages that passed relayer verification without corresponding on-chain XRPL balances. FBI IC3 complaint filed. Bridge paused and offline as of August 12.
#29 · Allbridge — Phantom CCTP Deposit / Base Router Drain — $191,156August 19–22, 2026 · Base (forged origin on Polygon) · Status: Contained Attacker 0x2419432344b0b892e592b2601b98eae702ba360e forged a CCTP-style message on Polygon declaring a 1,000,000 USDC transfer that never existed, then replayed the forged attestation on Base to credit his EIP-7702 account with 189,752 USDC withdrawn from Allbridge's Base router. Net extracted: $191,156. Detection credited to both Defimon and SlowMist.
#30 · ICON Network — Signature Replay Attack — $181,500August 27, 2026 · ICON · Status: Contained Between 02:01:02 and 02:21:12 UTC on August 27, an attacker replayed two legitimate withdrawal messages 1,492 times against ICON Network's bridge infrastructure, minting 119.866M ICX and 531,600 bnUSD. Net extraction after ICON Foundation freeze: ~150.2 ETH + 31,204 USDC = $181,500. The ICON Foundation froze the attacker's on-chain position within 20 minutes.
── TIER 6 · LOW (< $100K) ──
#31 · USM Protocol — Split-Invariance Flash Loan Exploit — $136,000August 9, 2026 · Ethereum L1 · Status: Contained USM Protocol was exploited for 70.830977 ETH (~$136,000) via a split-invariance arithmetic vulnerability in its ethFromDefund() redemption function. Attacker EOA: 0xb92b2E47680c89DA8f951B8963ef469f461a50Fc.
#32 · FoxMarket — Flash Loan Stale Spot-Price Bond Mint — $118,700August 15, 2026 · BNB Smart Chain · Status: Closed At block 116,169,049, attacker 0x5670d36f00bc7f6860b6afddb288e3668efc0ef9 exploited FoxLpBondsPool.stake() via a flash loan that exploited stale AMM spot price in a time-of-check / time-of-use flaw. Net extracted: ~119.14K USDT ($118,700).
#33 · Ethereum Address Poisoning — 82-Day Lookalike Preparation — $100,012August 11, 2026 · Ethereum L1 · Status: Active A victim lost 100,100 USDT ($100,012) to an address poisoning attack prepared over 82 days across three simultaneous layers: dust-attack transactions since May 21, 2026; lookalike address generation; and transaction history poisoning. Funds moved to Tornado Cash 72 seconds after receipt.
#34 · Full Sail (Sui) — Switchboard Oracle Key Compromise — $91,000August 29, 2026 · Sui · Status: Closed The same Switchboard oracle signing-key compromise used in the Virtue IOTA incident (August 28) was used one day later against Full Sail on Sui. Manipulated price feeds enabled undercollateralized borrowing; $91,000 extracted. Full Sail shut down the protocol entirely; users 100% reimbursed from protocol reserves. → See Cluster Analysis Section 3
#35 · StrongBlock — Abandoned Governance Takeover — $72,000August 5, 2026 · Ethereum · Status: Closed StrongBlock — a DeFi Nodes-as-a-Service protocol effectively abandoned since 2022 — retained an active on-chain Governor contract with its STRONG governance token trading near zero. Attacker 0xACBCa357981870f30130B145762d671891CA810c swept 32,695.76 STRONG + 383,447.17 STRNGR in a single transaction across blocks 25,691,519–25,691,700 (~3 minutes). Total: $72,000.
#36 · Nesa Chain — Cosmos EVM Underflow (GHSA-7g4w-cg88-2cq2) — $60,000 NetAugust 24, 2026 · Nesa (Cosmos EVM) · Status: Contained Attacker 0x9AE755D23Fc948fE94C9364A2398fd508a2AB0d2 (funded via Monero for obfuscation) exploited the same Cosmos EVM shared vulnerability against Nesa, inflating a balance to approximately $50M nominal before bridging to Ethereum. Net realized profit: $60,000, reflecting the severe illiquidity of NES tokens at scale. Identified independently by Bubblemaps. → See Cluster Analysis Section 3
#37 · Atomic Green — Uniswap V3 LP Signature Replay — $29,984August 8, 2026 · Arbitrum (L2 EVM) · Status: Contained Attacker EOA 0xf8803DaE13A6757E53711214769B5fb52Ec26C7E exploited a signature replay vulnerability in Atomic Green combined with a flash-loan price manipulation targeting Uniswap V3 LP positions. Net extracted: 29,984.27 USDC.
#38 · Float Protocol — Flash Loan Hypervisor Attack — $28,000August 31, 2026 · Ethereum · Status: Contained Attacker 0xAEA29218262dc6b0904Ca077f6527C49dfd426D9 used a flash loan to manipulate Uniswap V3 slot0 spot price feeding Float Protocol's Hypervisor contracts (no TWAP validation). 10.71 ETH extracted, 10 ETH immediately moved to Tornado Cash. Total: $28,000.
#39 · Panther Protocol — Reality.eth Governance Drain — $14,313August 6–7, 2026 · Base (Ethereum L2) · Status: Resolved Panther Protocol's Base deployment used Reality.eth as an optimistic governance oracle. A security safeguard designed to disable the Reality.eth module when no active governance existed was inadvertently removed in a prior upgrade. Attacker 0x7dB4cFea07042ca13a8E26cC90BbB59982Fe95B6 exploited this absence to execute an unauthorized governance proposal, sweeping 5,124,773.63 ZKP + 0.123 ETH. Total: $14,313. Resolved with a protocol upgrade restoring the safeguard.
SECTION 2B — NON-FINANCIAL INCIDENTS (16)
Sixteen incidents generated no confirmed financial loss but carry significant infrastructure, supply-chain, or threat-landscape implications:
Oraichain ICS-20 EVM Precompile Unauthorized Mint (Aug 8–12) — ~1.51B ORAI minted via ICS-20 EVM precompile; full recovery via chain-level roll-back; $0 net. Status: Recovering.
MANTRA Chain — Cosmos-EVM Module Exploit (Aug 21–22) — Attacker mantra13n9sk3p8x7tpq9adgxvzv9q0qev953mld0hwva displaced 720.9M OM from two accounts; full recovery via chain halt + freeze; $0 user loss. Status: Resolved.
Trezor / ShipMonk Data Breach (Aug 13) — 13,689 Trezor customer records exposed via Metabase SQL injection zero-day at fulfillment partner ShipMonk. Attributed to ShinyHunters. No funds lost.
SafePal Data Breach (Aug 16) — 39,798 customer records exposed via authorization flaw in a third-party order-tracking plugin. Data reportedly resold. No wallet or fund compromise.
Bits of Gold Data Breach (Aug 16–17) — ~200,000 customer records exposed via unauthorized access to a third-party analytics/support system. Part of a broader campaign. No funds affected.
BTCPay Server LND Macaroon Credential Exposure (Aug 7) — Critical unauthenticated vulnerability allowing access to LND .macaroon credential files; active exploitation confirmed. Total loss undisclosed. Status: Active.
npm Shai-Hulud Wave 6 (keyv/cacheable ecosystem) (Aug 4–5) — GitHub account compromise of maintainer "jaredwray"; 868+ packages / 1,381 versions affected; Ethereum used for C2 resolution. No confirmed crypto theft.
Rust Crates Supply Chain Attack (Aug 20–21) — Malicious proc-macro1 v1.0.107 published; arrayref@0.3.10, internment@0.8.7, append-only-vec affected (245M+ cumulative downloads for arrayref). No confirmed exploitation.
Solidity Pro VS Code Extension — Credential Stealer (Aug 6–19) — Two malicious extension accounts targeting Web3 Solidity developers; auto-updated every 30 minutes; seed-phrase and credential harvesting. No confirmed fund theft.
Coldcard-Themed "Hardware Wallet Audit" Phishing Campaign (Aug 3–5) — ScreenConnect RAT delivered via fake Coldcard audit emails, exploiting Coldcard disclosure anxiety. Documented by Proofpoint. No quantified losses.
Ravencoin KAWPOW Consensus Flaw & Chain Rollback (Aug 7–11) — Input validation flaw in C++ KAWPOW PoW code; invalid blocks accepted; 3–4 day chain rollback. First invalid block: height 4,487,776. RVN price −18–19%.
ZEUS Lightning Wallet Infrastructure Compromise (Aug 5–7) — Internal infrastructure attack against ZEUS (non-custodial Lightning wallet/LSP); successfully mitigated; $0 user loss. Status: Resolved.
Boltz Bitcoin Bridge — AI-Assisted Attack Suspension (Aug 3–4) — Escalating automated attacks on Boltz's non-custodial swap infrastructure; service voluntarily suspended; $0 user loss. Status: Paused.
Grok "Cryptographic Context Injection" (CCI) Vulnerability (Aug 19–20) — Adversa AI responsible disclosure: AES-256-GCM ciphertext on malicious web pages bypasses Grok's content classifiers, enabling chat data exfiltration. Reported June 3; not fully remediated as of August 20.
KITE Foundation Token Attack — Detected and Contained (Aug 6) — Automated monitoring flagged unauthorized KITE token transfers; all transfers suspended; $0 loss confirmed. Status: Contained.
Permapod (ZIGChain) — Incident Confirmed, Amount Undisclosed (Aug 29) — Incident confirmed via official X account; no financial figures, attacker addresses, or technical vector disclosed. Status: Active.
SECTION 3 — CLUSTER ANALYSIS
CLUSTER A — COSMOS EVM SHARED MODULE VULNERABILITY (GHSA-7g4w-cg88-2cq2)
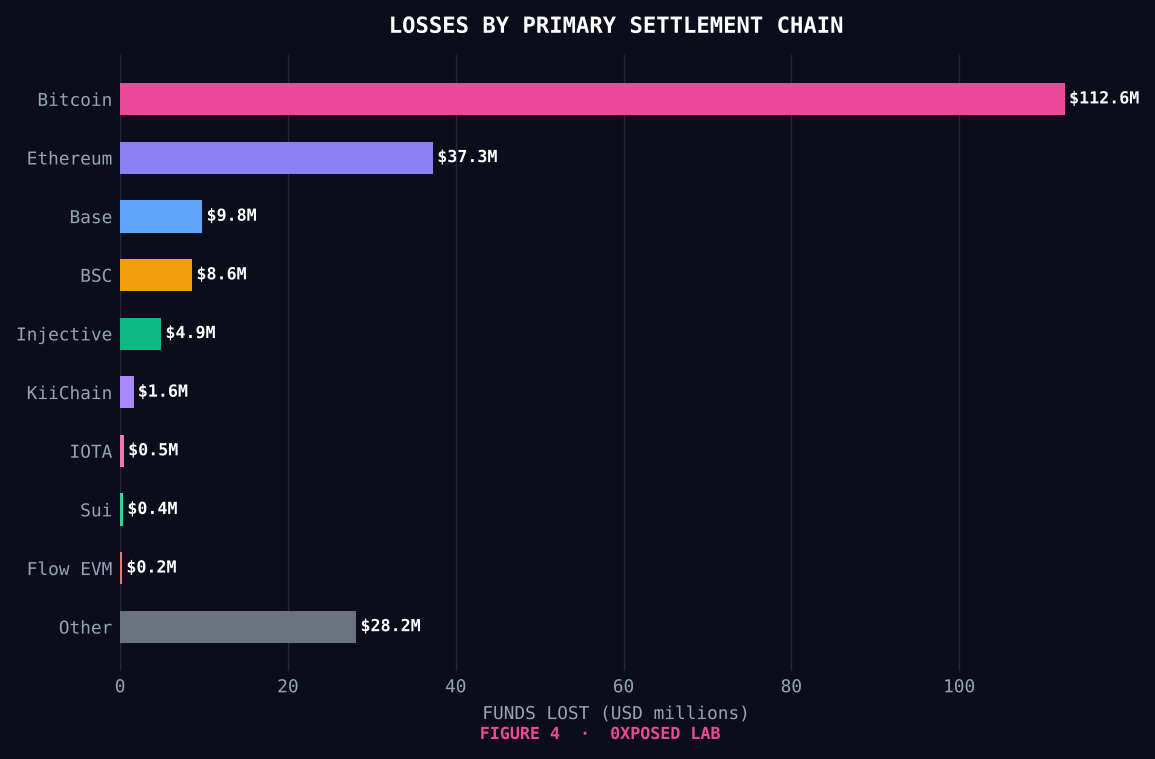
Three Cosmos EVM chains exploited via the same module vulnerability within 72 hours. Total confirmed loss: $2,675,774. This is a textbook shared-library supply-chain risk materializing across an ecosystem simultaneously.
On August 22–24, 2026, three separate Cosmos EVM-based chains — TAC, KiiChain, and Nesa — were exploited using the same underlying vulnerability GHSA-7g4w-cg88-2cq2: a balance-handling underflow in the shared Cosmos EVM module that allowed an attacker to precompute a deployment address, manipulate internal balance accounting, and withdraw tokens in excess of actual holdings. The attack sequence:
TAC — Aug 22, 19:46 UTC · Block 24,671,475 · $1,005,774 realized (of $7.5M nominal). Bridged to BNB Chain and TON.
KiiChain — Aug 22, ~20:32 UTC · 18 exploit attempts · 148,326,583.15 KII confirmed · $1,610,000. Only chain to publish exact token volumes.
Nesa — Aug 24 · Attacker: 0x9AE755D23Fc948fE94C9364A2398fd508a2AB0d2 (funded via Monero) · ~$50M nominal / $60,000 net. Identified by Bubblemaps independently.
MANTRA Chain — Aug 21–22 · Same vulnerability family; full recovery via chain halt and freeze. $0 net loss.
The 48-minute gap between the TAC and KiiChain attacks suggests either sequential exploitation or coordinated parallel activity. The Monero-funded Nesa attacker profile suggests a third distinct actor with better operational security. Cosmos Labs issued an ecosystem-wide patch advisory on August 25; all affected chains had patched or halted within 72 hours. CLUSTER B — SWITCHBOARD ORACLE SIGNING KEY COMPROMISE
Two protocols on two different chains — IOTA and Sui — exploited via the same compromised Switchboard oracle infrastructure within 24 hours. Combined loss: $546,000.
Virtue IOTA — Aug 28 · 14 compromised Switchboard oracle signing keys · 45 users liquidated · 47 liquidation events · 4.94M VUSD positions · $455,000.
Full Sail Sui — Aug 29 · Same compromised keys, different chain · $91,000 · Protocol shut down permanently; 100% reimbursed to users.
The 24-hour gap between IOTA and Sui suggests the attacker methodically deployed manipulation against each connected protocol in sequence. Switchboard issued an emergency key rotation advisory following the Full Sail incident. Protocols relying on Switchboard oracle infrastructure on Aptos, Movement, and Eclipse were advised to pause oracle-dependent functions pending key rotation confirmation. CLUSTER C — DEVELOPER TOOLING SUPPLY-CHAIN WAVE
Five separate developer-environment compromises in a single calendar month is not coincidence — it is a coordinated targeting of the upstream attack surface. When developers are the attack vector, every project they touch is downstream of the breach.
npm / keyv ecosystem (Shai-Hulud Wave 6) — Aug 4–5 · 868+ packages / 1,381 versions compromised via GitHub account takeover of "jaredwray." Ethereum C2 resolution.
Rust crates.io — Aug 20–21 · arrayref@0.3.10 (245M+ downloads), internment@0.8.7, append-only-vec published with malicious proc-macro1 dependency. 86–107 minute exposure window.
Solidity Pro VS Code Extension — Aug 6–19 · Two separate publisher accounts; auto-updated every 30 minutes; seed-phrase and credential exfiltration targeting Web3 developers.
BTCPay Server LND Macaroon Exposure — Aug 7 · Critical unauthenticated access to LND .macaroon files; active exploitation confirmed.
Coldcard Firmware RNG — $111M · Hardware-layer supply chain attack; RNG regression present since March 2021.
CLUSTER D — DATA BREACH TRIFECTA Three separate custodian data breaches in August exposed a combined ~253,487 user records:
Trezor / ShipMonk — 13,689 customer records · ShipMonk fulfillment partner · Metabase SQL injection zero-day (ShinyHunters attribution).
SafePal — 39,798 customer records · Authorization flaw in third-party order-tracking plugin · Data resold on underground markets.
Bits of Gold — ~200,000 customer records · Israeli regulated crypto broker · Third-party analytics/support system breach.
The convergence of hardware-wallet data breaches — spanning a Bitcoin signing device manufacturer, a software/hardware wallet provider, and an Israeli crypto broker — creates a uniquely dangerous threat environment for the exposed population, now a high-value target for spear-phishing, SIM-swapping, and physical location-based extortion.
SECTION 4 — AGGREGATE ANALYSIS
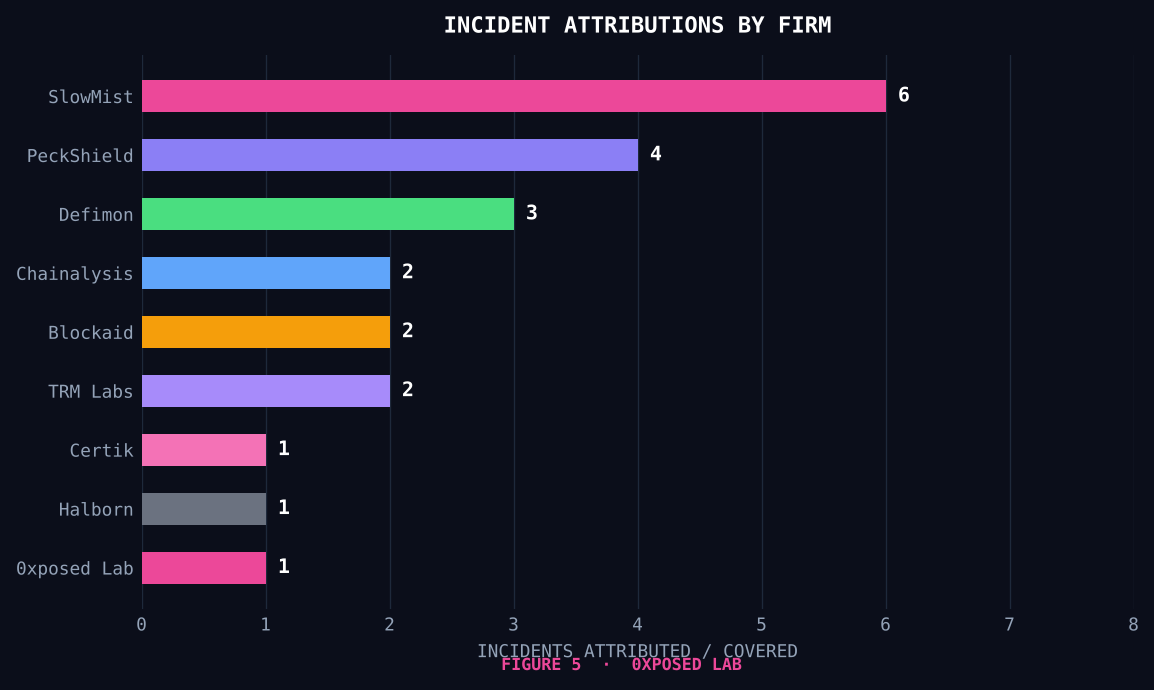
4.1 — LOSSES BY CHAIN / ECOSYSTEM Bitcoin dominates at $112,600,000 (55.2%), driven entirely by the Coldcard RNG firmware vulnerability ($111M) and the concurrent Trezor Google Ads phishing campaign ($1.6M). Remove the hardware-wallet vector entirely and Bitcoin-chain losses for the month approach zero. Ethereum (L1 + L2 ecosystem) accounts for $56,467,336 combined (27.7%) when aggregating Ethereum L1 ($37.3M), Base ($9.8M), and Arbitrum ($30K). Multi-chain incidents contributed $13,238,700 (6.5%). Cronos posted a rare $9.19M incident (Tectonic Finance). Injective at $4.9M represents the ecosystem's largest single exploit of the year. The Cosmos EVM cluster (TAC + KiiChain + Nesa) accounted for $2,675,774 — the most consequential single-vulnerability cross-chain event of August outside the Coldcard disclosure. 4.2 — LOSS BY ATTACK VECTOR
Private Key / Firmware compromise: $146,200,000 (71.7%) — Coldcard RNG, TLBL, Coinsbuy, Trezor phish, Fogo, Realio, StrongBlock
Price / Oracle Manipulation: $18,776,342 (9.2%) — Tectonic, Moonwell, Virtue IOTA, Full Sail, Term Finance, LoopsDAO, FoxMarket
Smart Contract Bug / Logic Flaw: $12,251,631 (6.0%) — Injective, BounceBit, Maya, MOKE, RISEx, Allbridge, ICON, Panther, Atomic Green, Ankr
Flash Loan / AMM Exploit: $10,462,596 (5.1%) — LoopsDAO, USM, Ajna V2, Balancer V1, Float, FoxMarket
Phishing / Social Engineering: $7,361,651 (3.6%) — Tornado Cash phish, Tiffany Milanovich, Base Drain, ETH address poisoning
Consensus / Protocol Bug: $4,500,000 (2.2%) — Harmony, Radix
Cosmos EVM Shared Vulnerability: $2,675,774 (1.3%) — TAC, KiiChain, Nesa
Bridge / Cross-chain Logic Flaw: $730,000 (0.4%) — Coreum, GOLD token / Solana
The dominance of the private key / firmware vector is anomalous — driven by the Coldcard disclosure. Absent that single event, flash loan and smart contract exploits collectively (~11%) would lead the chart, consistent with the structural DeFi exploit pattern observed since 2024.
SECTION 5 — DETECTION & RECOVERY ANALYSIS
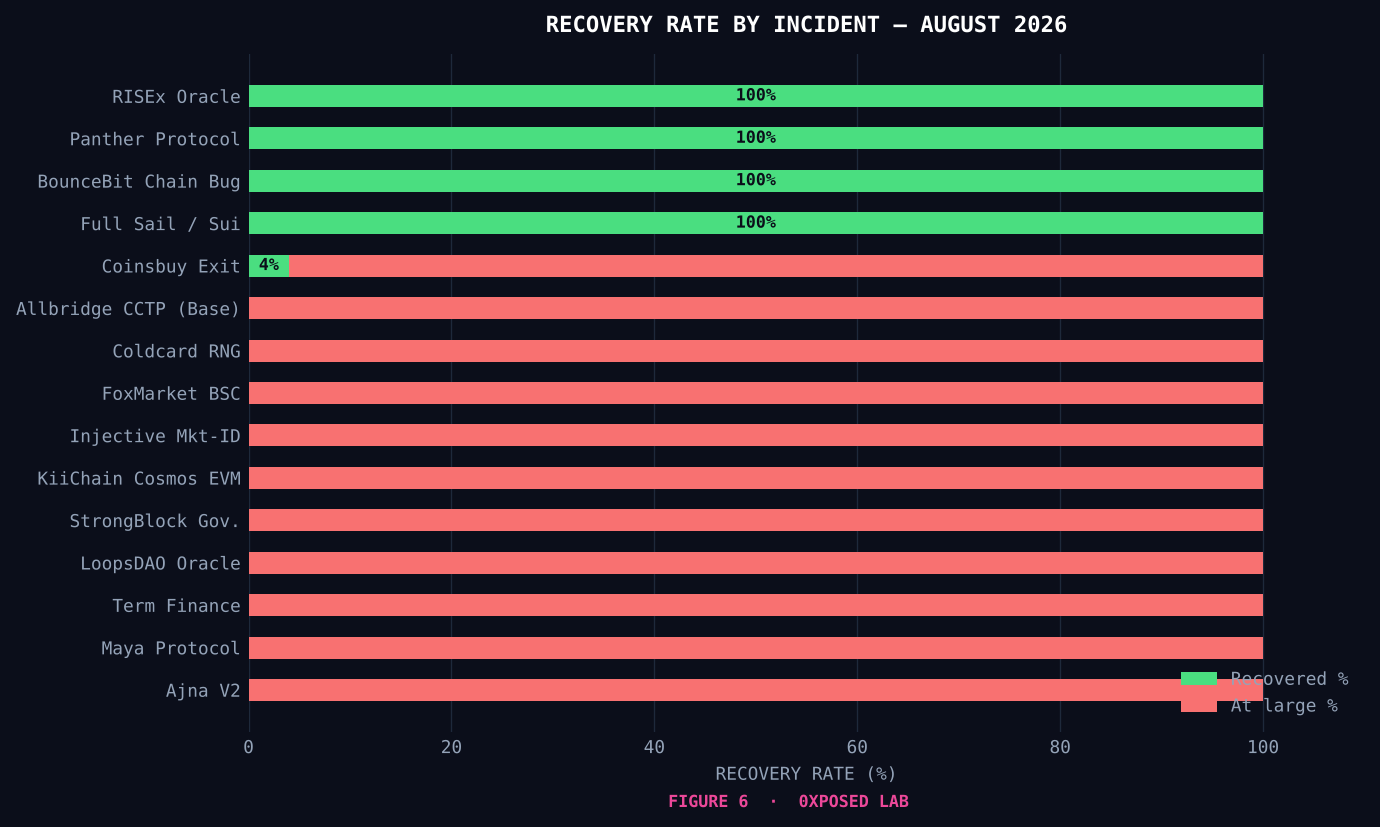
5.1 — RECOVERY RATE$0 formally recovered from confirmed financial losses in August 2026. This is unusual even by crypto standards: typically 2–8% of monthly losses see partial protocol-level recovery or white-hat return within the reporting month. Notable recovery-adjacent outcomes:
Full Sail (Sui) — $91,000 loss but 100% reimbursed to users by the protocol from reserves (not on-chain recovery from the attacker). Net user impact: $0.
MANTRA Chain — 720.9M OM displaced but fully frozen and recovered via chain halt. $0 net user loss.
Oraichain — 1.51B ORAI minted but contained via chain-level rollback. $0 net user loss.
5.2 — DETECTION PATTERNS Defimon pre-flagged two exploits before they were executed: Allbridge CCTP (detected the forged message) and Ajna V2 (vulnerability flagged pre-attack). In neither case did the warning lead to a successful prevention — the speed of on-chain execution outpaced human response latency. This highlights a core gap: detection is not the bottleneck; automated circuit-breaker mechanisms are. The Ajna V2 case is the starkest example of the month: Defimon flagged the vulnerability on Discord more than one hour before the attack. The alert went unread, unresponded to, and unactionable. The exploit proceeded, draining $775,400 from seven immutable pools. Automated detection without automated response provides false assurance. 5.3 — INCIDENT STATUS DISTRIBUTION
Active: 9 financial incidents (Coldcard, TLBL, Injective, Tornado Cash phish, Trezor phish, Tiffany Milanovich, MOKE, Ajna, ETH Address Poisoning) — no resolution path announced
Contained: 15 financial incidents — attack vector closed, losses confirmed, no recovery
Closed: 5 financial incidents — protocol sunset or formally closed (BounceBit, LoopsDAO, Full Sail, StrongBlock, Base Drain)
Resolved: 4 financial incidents — protocol operational, affected users compensated (Coinsbuy, RISEx, Panther, Ankr)
Paused: 3 financial incidents — operations suspended pending patch (Maya, Coreum, Harmony)
Recovering: 3 financial incidents — partial mitigation in progress
SECTION 6 — RECOMMENDATIONS
6.1 — For Hardware Wallet Users (Coldcard / Trezor Phishing cluster)
Check your Coldcard firmware version immediately. If you generated seeds on v4.0.1 or later (pre-patch), migrate to a fresh device with updated firmware and new seed generation.
Verify any Trezor-related communications or software via the official trezor.io domain only — not Google Ads results, not Google Sites-hosted pages.
Treat any unsolicited "wallet audit" or "firmware verification" request as a phishing attempt, particularly in the weeks following a high-profile hardware disclosure.
6.2 — For Cosmos EVM Chain Operators
Audit your Cosmos EVM module version against the GHSA-7g4w-cg88-2cq2 patch immediately. Any chain running the unpatched module is a viable target.
Implement automated balance-invariant monitoring that halts withdrawals if cumulative outflows exceed on-chain liquidity within a configurable time window.
Coordinate vulnerability disclosure cross-chain: the 48-minute gap between TAC and KiiChain exploits suggests sequential targeting; simultaneous disclosure and patch deployment could have prevented later incidents.
6.3 — For DeFi Protocols (Oracle / Flash Loan / Governance)
Moonwell, Tectonic, and Allbridge all share a common failure mode: price or state manipulation bypassing supply caps through donation attacks or forged cross-chain messages. Time-weighted average price (TWAP) oracles over 15–30 minute windows eliminate spot-price manipulation.
Governance proposals funded via Tornado Cash wallets (Term Finance) should trigger automatic quarantine delays. On-chain provenance tracking of governance participants is a viable and proportionate response.
Deploy Defimon-class monitoring with automated circuit breakers: detection without automated response is insufficient, as demonstrated by the Ajna V2 and Allbridge incidents.
6.4 — For Developers (Supply Chain Wave)
Audit your npm and Rust dependency trees for keyv@6.0.0 and affected crates (arrayref@0.3.10, internment@0.8.7, append-only-vec) — update immediately.
Remove Solidity Pro VS Code extension (publisher accounts helper-beeps.solidity-pro and web3devtoolsx.solidity-pro) if installed. Treat any IDE extension not from a verified publisher with extreme caution.
Implement reproducible builds and dependency pinning (locked package files, hash verification) as standard practice for all Web3 tooling.
6.5 — For Crypto Customers (Data Breach Trifecta)
If you purchased a Trezor, used SafePal, or have an account with Bits of Gold: assume your shipping address, email, and phone number are in the hands of threat actors. Enable two-factor authentication everywhere and be highly suspicious of any wallet-related communication by phone or email.
Consider a physical address update for any crypto hardware delivery — your shipping address is now a known data point for social engineering campaigns targeting high-value crypto holders.
CAVEATS & METHODOLOGY
All financial figures are sourced directly from the incident JSON data provided to 0xposed Lab. No amount has been estimated, extrapolated, or approximated without JSON-sourced documentation.
The $204,026,958 total covers 55 incidents (53 valid after excluding one duplicate Injective entry and one September event misclassified as August). 39 incidents carry confirmed financial losses; 16 are non-financial.
"Net" vs. "gross" distinctions are applied where the JSON explicitly notes the difference (e.g., Tectonic $120M gross / $9.19M net; Fogo $3M gross / $1.2M net; Realio $6.2M gross / $338.7K liquid).
Recovery figures reflect on-chain data as of the incident dates. Subsequent off-chain settlements, insurance payouts, or exchange freezes are not included.
Coinsbuy ($7.9M) is classified as multi-chain (Ethereum + TRON) for chain attribution purposes.
The Liquid Network incident originally included in the dataset was excluded — it occurred in September 2026 and falls outside the August reporting window.
The duplicate Injective entry (3e4e73eb-incident_17_injective__1_.json) was excluded; only the primary entry (e48b20c0-incident_17_injective.json) is counted.
The DeFi Llama figure for Virtue IOTA ($894,500) has not been reconciled with Virtue's official $455,000 figure. We use Virtue's published figure with the discrepancy noted.
0xposed Lab aggregates and publishes this report for educational and research purposes. Nothing herein constitutes financial, legal, or investment advice. All incident figures are sourced from public disclosures; 0xposed Lab does not independently verify chain-of-custody or law enforcement referrals.
0xposed Lab — Blockchain Threat Intelligence0xposed.io/radar · @0xposed_lab